AI Insights Architecture Overview
This section applies to Foglight® for Databases (on-premises or Foglight Cloud) and explains how it communicates with Foglight AI Insights.
Foglight follows a standard monitoring model: agents collect telemetry from monitored targets and send it to the Foglight Management Server (FMS) for processing, correlation, and reporting. The Foglight MCP Server is part of that same Foglight platform, alongside FMS and the Repository, and it exposes selected capabilities as MCP tools. Foglight AI Insights (the AI client) does not connect directly to the monitoring environment; instead, it connects through the MCP Server, which calls Foglight’s APIs and returns structured results, without exposing the monitoring environment directly.
In a Foglight Cloud deployment, Foglight AI Insights and the MCP Server are all hosted in the Cloud, so AI Insights can connect directly to the cloud-hosted MCP Server over an encrypted channel.
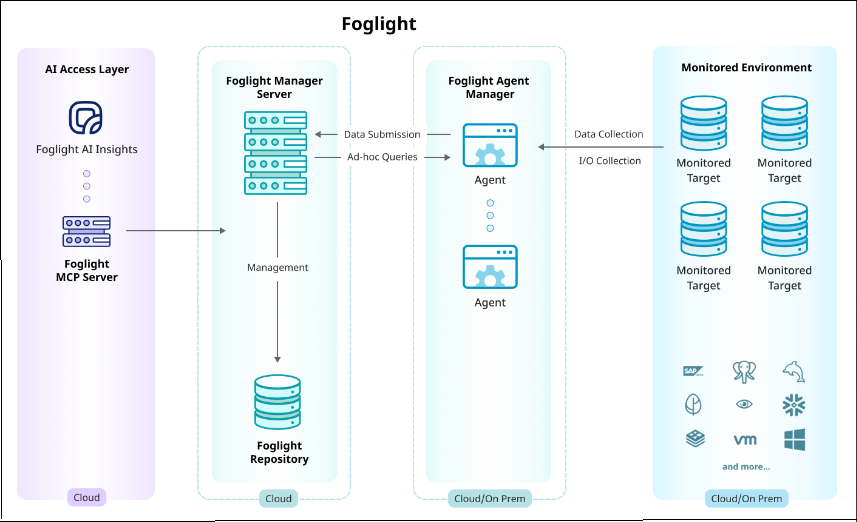
To learn about the ability of Foglight AI Insights to connect to Foglight on-premises, see the on-premises Architecture Overview🔗.
This design does the following:
- Keeps AI access within the managed Foglight Cloud boundary.
- Removes the need to expose or configure on-premises endpoints.
- Uses cloud-native authentication and encryption to keep AI access controlled and authenticated.
How the architecture works
The following steps describe how monitoring data flows from your environment to the AI client:
- Monitoring agents collect telemetry from the target environment.
- The Foglight Agent Manager forwards the telemetry to Foglight Cloud.
- Foglight Cloud stores, correlates, and serves the data through Foglight APIs and related services.
- The AI client connects directly to the cloud-hosted MCP Server.
- The AI client calls supported tools, such as alarm checks, PI queries, TopSQL analysis, or GraphQL topology searches.
- The MCP Server calls the relevant Foglight API or service and returns the results to the AI client.
This flow aligns AI access with your existing Foglight Cloud platform instead of replacing it.
Security boundaries
The architecture maintains clear boundaries between the following layers:
- The AI client layer
- The MCP integration layer
- The Foglight Cloud platform and its APIs
- The monitored infrastructure and telemetry collection layer
These boundaries let the AI client access operational data while Foglight Cloud retains full governance and control. The AI client never calls monitoring APIs directly. The MCP Server always acts as the controlled intermediary.

